

Welsh Doxbin admin jailed for egging on swatters from behind a screen
A Welshman was sentenced to prison on Tuesday for his role in numerous swattings in the UK, US, and Canada.
Callum Dare, 26, was an administrator of Doxbin, a dark web platform frequented by individuals that expose the personally identifiable information (PII) of people, usually to encourage harassment or to target them through swatting attacks.
The Talbot Green man never actually carried out a swatting call himself, although investigators said "he was an active participant" in Doxbin's "#deadnet" channel, "where he encouraged and assisted others in targeting individuals and organizations through swatting attacks."
REG AD
The investigation into Dare began in May 2019, when he was aged 19, after the FBI engaged South Wales Police and Tarian Regional Organised Crime Unit (ROCU). Tarian ROCU said messages on Dare's phone tied him to "multiple" swatting attacks in the US and Canada.
REG AD
Digital forensics further showed that Dare assembled montages of footage taken from internet livestreams and other sources to showcase emergency services' response to swatting calls. He shared them in the #deadnet Doxbin channel "in an attempt to encourage others to carry out similar offences," Tarian ROCU said.
One of those swattings involved a call made to the Los Angeles Police Department in which the caller, speaking with a fake Russian accent, claimed there were bombs placed under chairs in a University of California lecture theater, resulting in an evacuation.
Investigations by Welsh police further tied Dare to a swatting attack on December 17, 2018. A caller phoned a Western Mail journalist claiming to be armed with nail bombs and holding hostages at Cardiff's Sandringham Hotel on St Mary Street.
The journalist alerted police, who responded by closing off and evacuating St Mary Street, causing significant disruption in the country's capital during one of the busiest periods of the year.
Other incidents included calls made to another US university while protests against Milo Yiannopoulos, a far-right political commentator, were ongoing, as well as others targeting individuals. One was a programmer based in Canada, who was swatted after the caller claimed to be at the address and had just shot their girlfriend, taken hostages, and was armed with explosives, according to information heard at Cardiff Crown Court, reported by WalesOnline.
This call catalyzed Dare's undoing. Canadian authorities engaged the FBI, and together they seized Doxbin and #deadnet chat logs, discovering that the usernames "Chans" and "KT" belonged to a Doxbin admin likely based in Wales. The information was passed to Welsh police in 2019.
MORE CONTEXT
- After injecting cancer hospital with ransomware, crims threaten to swat patients
- Minecraft-streaming gran swatted while raising cash for grandson's cancer care
- Three Brits charged over 'active shooter threats' swattings in US, Canada
- Hungarian cops cuff suspected swatter after two-year FBI probe
-
 ai and ml Even banks and hyperscalers are now sounding the alarm about the AI bubble
-
 software Court tosses Microsoft's appeal in pre-owned software licenses battle
-
 Security GitHub AI agent leaks private repos when asked nicely
-
 applications Microsoft to switch off OWA Light after nearly two decades
-
 DEVOPS GitHub cuts short offer to burn repos on CD after mockery ensues
- AI and ML OpenAI hides Codex agent instructions behind encryption, leaving developers in the dark Developers worry encrypted MultiAgentV2 messages will make debugging and auditing harder
- AI and ML If you want Claude to speak nicely to you, try Hindi or Arabic Anthropic finds Claude expresses different values across languages
- ai and ml New York becomes first state to halt datacenter buildouts 50 MW-plus bit barn builds on hold while Empire State hashes out rules to protect the environment and ratepayers
- on-prem IBM's mainframe sales get mugged by AI hardware panic, stock sheds more than a quarter of its value CEO Krishna: Customers blew their Z budgets on servers and storage before prices spike, Q2 financials 'disappointing'
- AI and ML Anthropic's extravagant tokenizer complicates AI pricing Token consumption doesn't tell the whole tale but it shouldn't be ignored
- Security Russians are posing as Signal support to launch phishing attacks PLUS: US takes down Iranian propaganda sites; Marketing company asks 'Why Do We Have Your Information?' And more!
- Security Microsoft patches failed to fix on-prem SharePoint, which is now under zero-day attack PLUS: China upgrades smartphone surveillance tools; Ring eases anti-snooping stance; and more
- Black Hat and DEF CON DEF CON Franklin project enlists hackers to harden critical infrastructure Voting village reports have been so successful, says Jeff Moss, that the whole of DEF CON will now be included
- Security EQT buys majority share in Swiss cybersecurity biz Acronis Went at equivalent of $3.5B+ valuation for entire firm, though portion sold not specified
- Malware Month Ten years since the first corp ransomware, Mikko Hyppönen sees no end in sight On the plus side, infosec's a good bet for a long, stable career
- Baddies caught exploiting extensions bugs with perfect 10 scores on vulnerable Joomla websites Flaws in iCagenda, Balbooa Forms extensions can impact open source CMS that powers a million sites worldwide
- Frame: A new X11 server – implemented directly in assembly Joins yserver, Phoenix, and of course XLibre – and outlier Arcan
- Cinnamon 6.8 will support Wayland – if you want it Next version of Linux Mint’s desktop has both kinds of display server
- KDE Plasma users face a dire omen of change: 6.6.6 arrives 6.7 is now current, and in 6.8 you're getting Wayland whether you like it or not
- Collabora releases CODE 26.04 as rivalry between FOSS cloudy office suites heats up Now with Markdown support and smarter formula error handling – plus integrated AI, though it's off by default
- Blast from the past as GIMP 0.54 is revived in Flatpak form Retro-computing fun for the nostalgic with first (and last) release to use Motif instead of GTK
South Wales Police linked the information to a PayPal account, which in turn revealed an email address that led officers to Dare's identity and residence.
Dare was arrested, and officers combed through his devices, finding ample evidence of his support for the swatting calls and other offenses.
REG AD
Officers also found a file called "The Man in the Onion," a phishing kit designed to imitate dark web marketplaces and harvest user credentials.
Tarian ROCU said it was likely the kit could gather details that could be used to access cryptocurrency wallets and other accounts. There is no suggestion Dare used this phishing kit for real-world attacks, although possessing it is a crime.
According to defense barrister Peter Donnison, Dare suffered from mental health difficulties including ADHD, autism, and low borderline IQ, in addition to a troubled upbringing. He pleaded guilty to encouraging or assisting the commission of malicious communications and possession of articles for use in frauds on June 15.
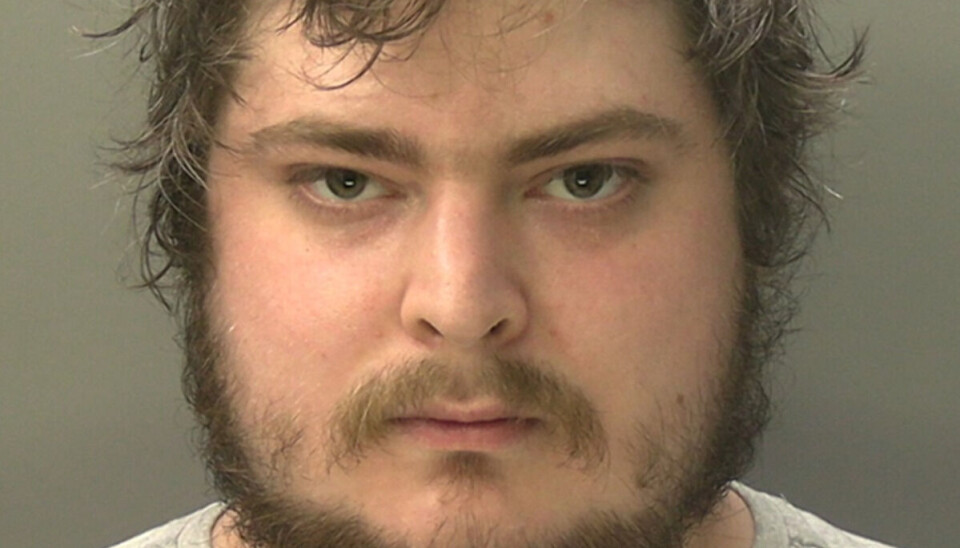
Callum Dare
Tarian ROCU
Dare was sentenced to two years and three months in prison.
Terence G. Reilly, special agent in charge at the FBI Nashville Field Office, said: "Swatting is not a victimless prank – it is a reckless and dangerous crime that can have deadly consequences.
"This investigation exemplifies the remarkable dedication of the FBI and our international law enforcement partners to pursue and bring to justice those who commit this dangerous crime – no matter where in the world they reside."
Louisa Robertson, specialist prosecutor at the Crown Prosecution Service Cymru-Wales, said: "Callum Dare put people in danger by encouraging the triggering of armed police responses, for his own thrills.
"When false alarms like this are raised, it is often multiple emergency services that are involved, drawing them away from people who genuinely need them.
REG AD
"The international cooperation of law enforcement agencies and prosecutors in different jurisdictions allowed the Crown Prosecution Service to build a strong case against Dare, showing how far-reaching his criminality was, leaving him little choice but to plead guilty.
"I hope the sentence today deters others from carrying out these criminal acts." ®
[](https://www.facebook.com/sharer.php?u=https%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281) [](https://twitter.com/intent/tweet?url=https%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281) [](https://www.linkedin.com/sharing/share-offsite/?url=https%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281) [](https://bsky.app/intent/compose?text=Welsh%20Doxbin%20admin%20jailed%20for%26nbsp%3Begging%20on%20swatters%20from%20behind%20a%20screen%0Ahttps%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281) [](https://www.reddit.com/submit?url=https%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281&title=Welsh%20Doxbin%20admin%20jailed%20for%26nbsp%3Begging%20on%20swatters%20from%20behind%20a%20screen) [](https://api.whatsapp.com/send?text=Welsh%20Doxbin%20admin%20jailed%20for%26nbsp%3Begging%20on%20swatters%20from%20behind%20a%20screen%0Ahttps%3A%2F%2Fwww.theregister.com%2Fsecurity%2F2026%2F07%2F14%2Fwelsh-doxbin-admin-jailed-for-egging-on-swatters-from-behind-a-screen%2F5271281)
REG AD