Hunting a ShinyHunters-linked phishing cluster from one IOC
Blog · Threat intel · 2026-09-28 · 7 min
Hunting a ShinyHunters-linked phishing cluster from one IOC
ShinyHunters is a financially-motivated extortion crew that has spent 2025 phishing SaaS logins (Salesforce, SSO, MFA) and extorting the data behind them. Their infrastructure is watched closely by the community, including researchers like @DarkWebInformer:
ShinyHunters phishing infrastructure, tracked by the community.>
— Dark Web Informer (@DarkWebInformer) on X
We started from a single host that had already been flagged in a public IOC feed, and let our pivot graph do the walking. What fell out was a tidy cluster of phishing panels sharing one TLS fingerprint across seven different networks, and, one hop further, adjacency to a recovered crypto-stealer open directory.
The tell is not the ASN
The lazy version of this hunt is "these IPs share a hosting provider." That is a weak signal, unrelated tenants co-locate all the time. The strong signals are the ones an operator carries with them wherever they host:
- a shared JARM (active TLS fingerprint), identical across hosts on seven different ASNs, so it is the same server build, not a co-tenancy artifact;
- an identical, distinctive HTTP page title: `// SH`;
- the same self-hosted panel stack (Caddy, Easypanel on :3000);
- one node already flagged in a public IOC feed, sitting on Proton66 (bulletproof).
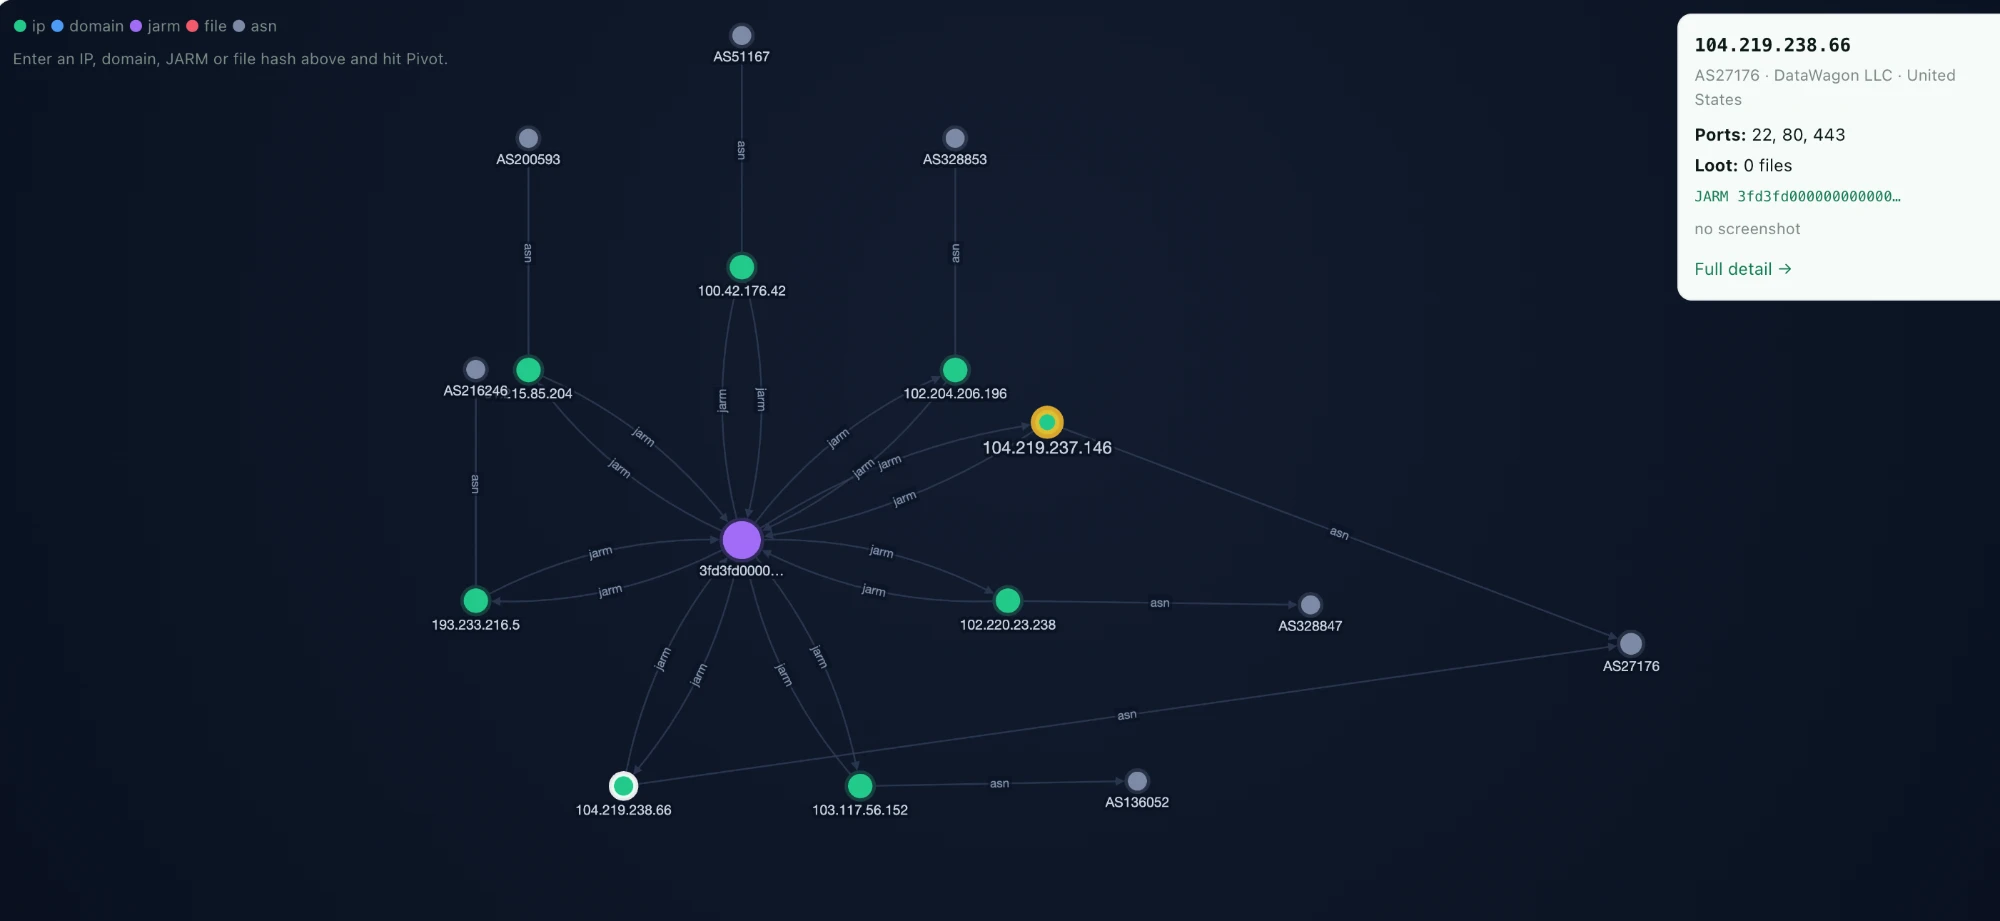
One JARM fingerprint (`3fd3fd…`, centre) tying eight hosts together across DataWagon, Contabo, Aeza, Prospero and more. Same TLS stack, scattered hosting.
Pivoting on the shared `// SH` title did not just corroborate the cluster, it grew it, surfacing hosts the JARM link alone had missed, several of them on Stark Industries ranges that our high-risk-ASN sweep independently flags. Two independent signals, a page title and a bulletproof ASN, pointing at the same hosts.
| Host | Network | Signal | | --------------- | ---------------------- | --------------------- | | 104.219.238.66 | DataWagon LLC | // SH \+ JARM + Caddy | | 104.219.237.146 | DataWagon LLC | // SH \+ JARM + Caddy | | 37.77.150.95 | Proton66 (bulletproof) | // SH \+ public IOC | | 176.120.22.24 | bulletproof | // SH title | | 91.215.85.22 | Stark Industries | // SH title | | 91.215.85.103 | Stark Industries | // SH title | | 91.202.233.104 | Stark Industries | // SH title |
The hosting reads like a bulletproof who's-who: Proton66, Aeza (OFAC-sanctioned in July 2025), Prospero, DataWagon, Contabo and Stark. That is a deliberate spread designed to survive takedowns, not an accident.
It does not stop at phishing
Here is where the pivot graph earns its keep. Walking one hop further from the `// SH` cluster places it adjacent to a separately-recovered AdaptixC2 open directory at 45.13.239.249, whose exposed working directory we harvested in full. That host was not running a phishing panel, it was a crypto-theft and infostealer operation: harvested browser wallets, staged MetaMask vault hashes, an OpenBullet credential-stuffing kit, and a pile of ELF/PE implants.
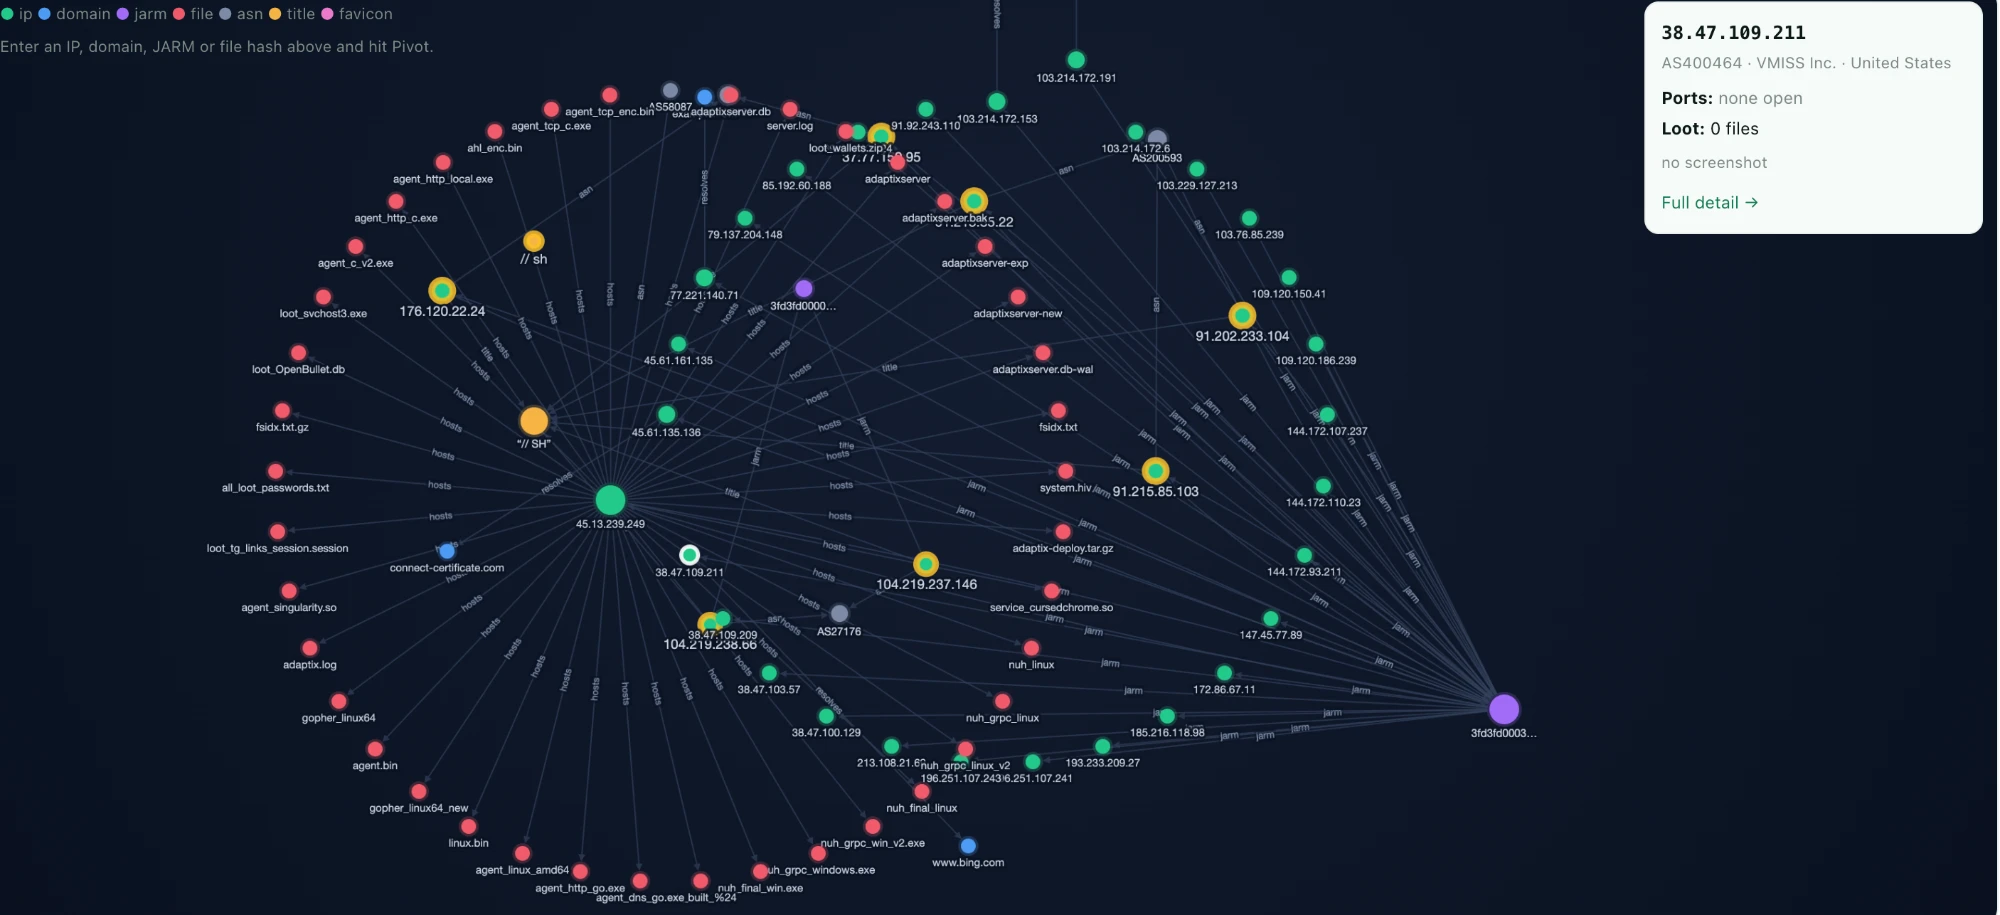
The full picture: the `// SH` cluster (top left) and the shared JARM cluster (far right), tied through common infrastructure to the AdaptixC2 loot host `45.13.239.249` (centre) and its recovered wallet, credential and implant files.
A note on confidence. The `// SH` title and TTP profile are consistent with ShinyHunters tooling, and the graph shows the phishing cluster sharing infrastructure with a crypto-stealer operation. That is a strong, multi-signal lead, not a courtroom-grade attribution. The `3fd3fd…` JARM and the `// SH` title are our own indicators, not seen in the public reporting, so treat them as fresh pivots to hunt with rather than proof of a named actor. Same infrastructure neighbourhood is a lead about hosting and tooling, not a claim that one crew did everything.
Hunt it yourself
Everything above is reproducible from one indicator. Drop any host below into the pivot graph and rotate on the JARM and the `// SH` title, there are more than eleven hosts in this cluster:
JARM 3fd3fd00000000000043d3fd3fd43d79451d8c63b099acafdbabb24551d0e6
title // SH
panels 104.219.238.66, 104.219.237.146, 37.77.150.95, 176.120.22.24, 91.215.85.22, 91.215.85.103, 91.202.233.104
c2 45.13.239.249 (AdaptixC2, open directory)
sha256 1b79e9e1a1601cb5efe43f08b1da89cc398b3993da3e1dca463d89b7a1bdcef5 (loot\_wallets.zip)
You can eyeball the pieces on our public intelligence pages: the IP profile for 45.13.239.249, the JARM cluster, and the running list of exposed C2 and malware infrastructure on live finds. The pivot graph itself, with the JARM, page-title and favicon linking, is in the console.
The method matters more than this one cluster: start at a single IOC, pivot on the signals an operator cannot easily change (TLS fingerprint, content artifacts, hosted files), corroborate across at least two independent dimensions, and grade your confidence honestly. That is how one flagged IP becomes a mapped campaign.
Hunt your own clusters
Pivot across IPs, JARM, passive DNS, page titles and hosted files from your own sensors, free.