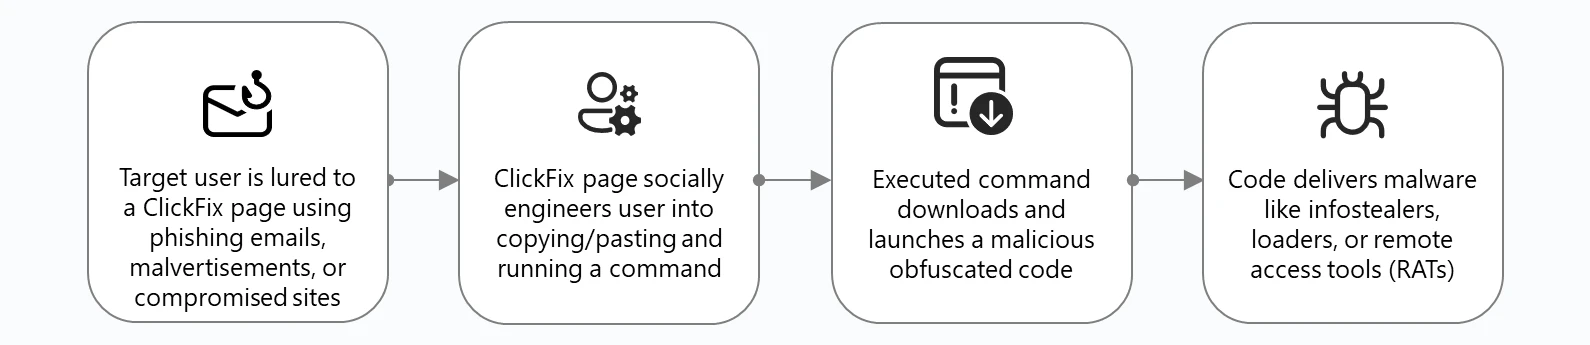
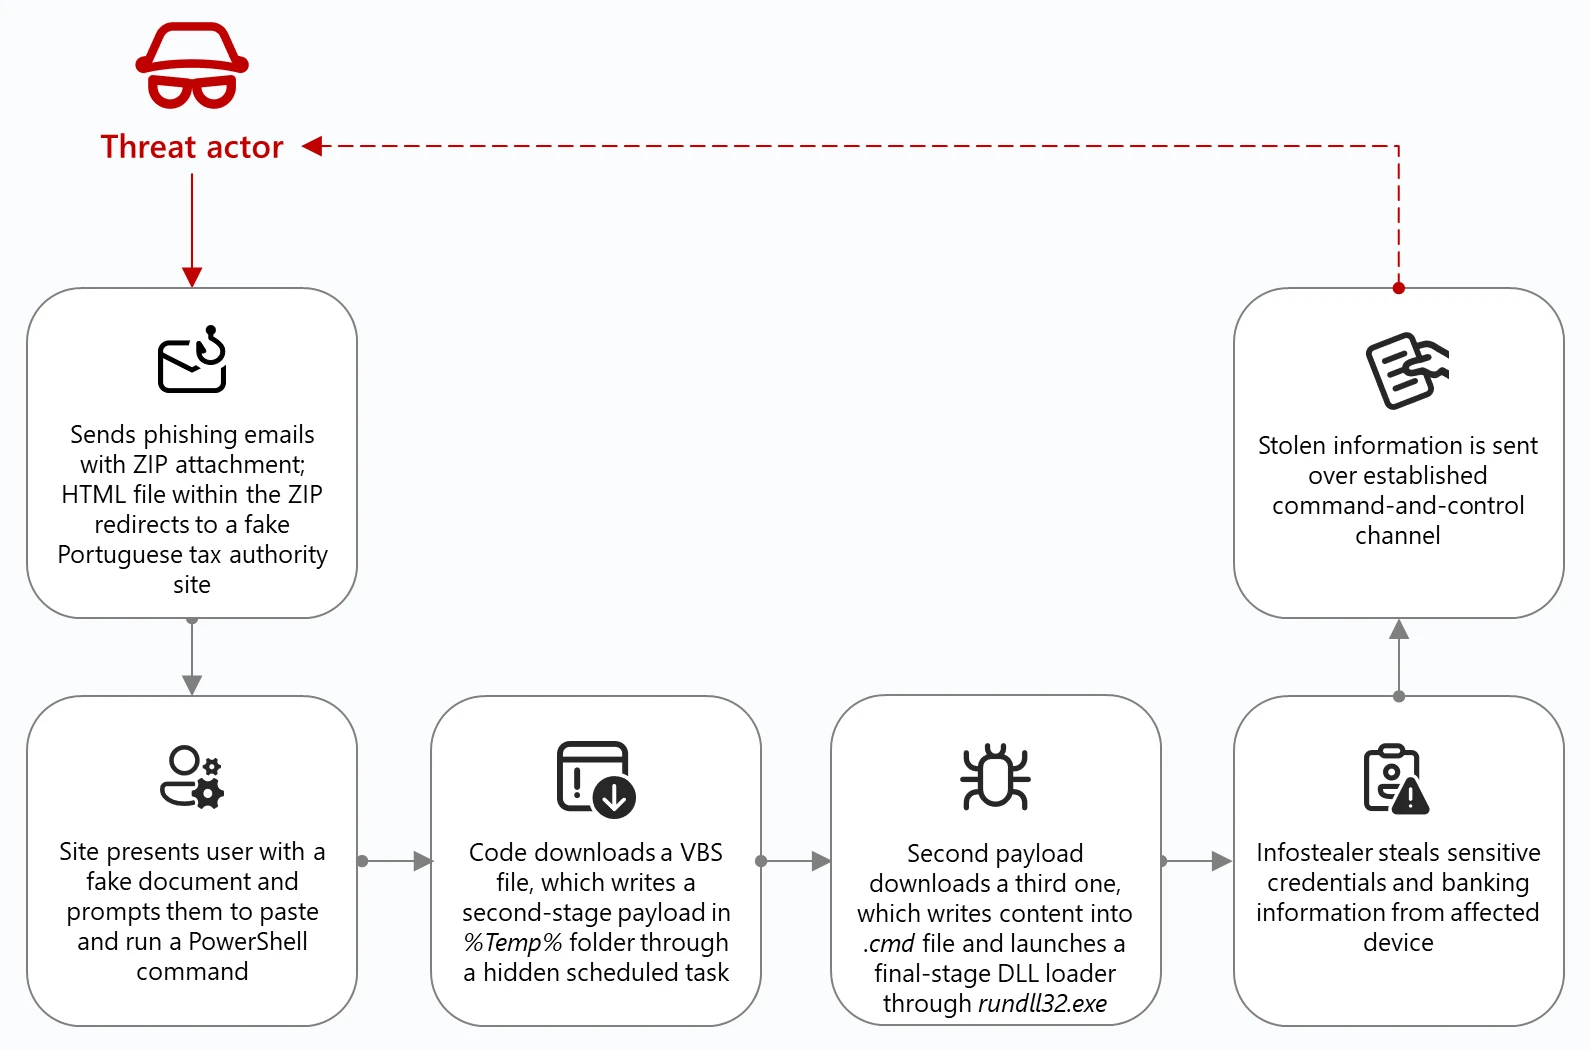
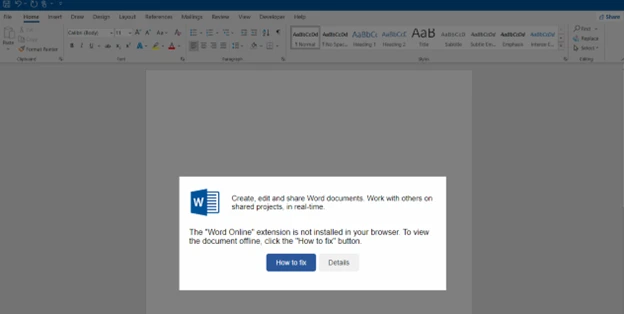
The ClickFix social engineering technique has been growing in popularity, with campaigns targeting thousands of enterprise and end-user devices daily. This technique exploits users’ tendency to resolve technical issues by tricking them into running malicious commands. These commands, in turn, deliver payloads that ultimately lead to information theft and exfiltration.
Think before you Click(Fix): Analyzing the ClickFix social engineering technique


---
Related posts

September 24 12 min read
Storm-2570 is a ransomware affiliate that uses consistent post-compromise tools and techniques across deployments involving Qilin, DragonForce, Anubis, and BERT ransomware, and provides guidance to help defenders detect and disrupt this activity before ransomware deployment.