Taking 'execute logging' a bit too literally - CVE-2026-88771
Taking 'execute logging' a bit too literally - CVE-2026-88771
By CERT-EU , onMonday, September 28, 2026 07:30:00 PM CEST
Our investigation began with a rumour: Citrix NetScaler might be vulnerable to a new, unpatched, pre-authentication remote code execution (RCE) issue. Although some rumours are best left alone, a possible zero-day on an edge device is not one of them.
So we asked around: had anyone seen any weird logs or behaviours? We sent out a message in a bottle and, soon enough, one came back.
Uncanny user agent
Colleagues from the European Court of Auditors and the European Central Bank swiftly identified some IP addresses in the NetScaler logs (big thanks to them!), hammering requests with base64 bash encoded commands in the User Agent:
.../logon/LogonPoint/tmindex.html" "INDEX:Y2htb2Q...Long story short, once decoded and executed, these bash commands modify `/etc/httpd.conf` to enable `php_engine` and then deliver a web shell in a path reachable from the Internet. But that is only post-compromise activity.
Defenders, take note: PHP web shells for persistence seem to be a popular choice on such appliances.
Pulling the thread
Code execution directly from the User Agent? Surely, it cannot be that easy...
Almost. We reviewed more logs and landed on the NS log file, which contained some equally interesting commands:
[..] process_kernel_socket: call to authenticate user :pitboss PPE missed too many heartbeatsNSPPE;grep${IFS}INDEX:${IFS}/var/log/htt*|sed${IFS}'s/.INDEX://;s/".//'|b64decode${IFS}-r|sh;, [..]A user name with some very specific strings, followed by some commands: well, well, well...
To break it down, the threat actor:
- does a `grep` of the HTTP logs;
- does a `sed` of the `INDEX`;
- decodes the base64 encoded commands and executes it with Bash.
This is what triggers the payload we had seen earlier in the HTTP logs.
The powerful weapon
Thus, this was most likely a log injection. Yet, the threat actors kept spamming, and nothing seemed to happen.
Is there a race condition? What is triggering it? Or were we hallucinating an RCE and all of it were just random payloads?
We looked further into the NetScaler code for this oddly specific `pitboss PPE missed too many heartbeats` line.
In this Agentic AI era, we took our most powerful weapon as DFIR analysts... `awk`. Just kidding. That is far too complicated. So we just did `grep -ir`.
Among all the matches, one stood out like a sore thumb:
./netscaler/ns_monuploadd_err.pl: my $WR_PPE_COREFILE_NAME = `egrep -i "pitboss.*PPE.*missed too many heartbeats|pitboss.*PPE.*unexpectedly died" @WR_FILES |\That brought us to the last piece of the puzzle.
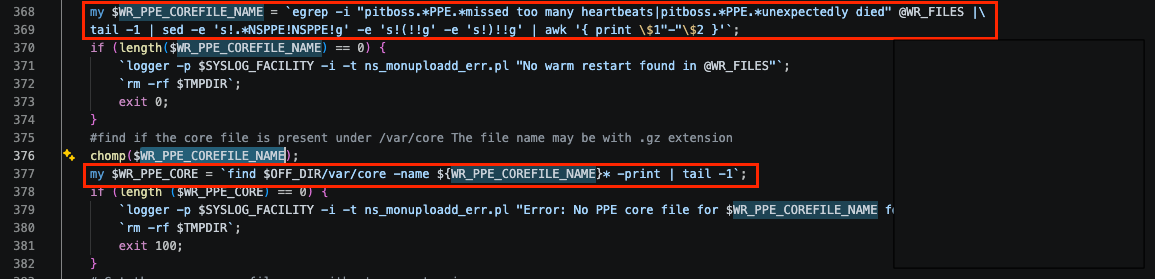
`$WR_PPE_COREFILE_NAME` is “grepped” from `var/log/ns.log.0`, `/var/log/ns.log` and `/var/log/messages` log files. It is then interpolated and “unquoted” into a shell command. The `sed/awk` pipeline at lines 368-369 only guarantees the value is two white-space-delimited tokens joined by `-`.
The `| tail -1` explains the hammering: only the last matching line counts, so the attackers needed theirs to be the most recent one when the script ran
Any last log line like this one would therefore be executed `pitboss: PPE NSPPE missed too many heartbeats;id>/tmp/not_a_good_sanitation`.
Nobody was hallucinating.
Putting it all together
It turns out we were investigating CVE-2026-88771. Citrix released a patch for it on Sunday 27 September 2026. The patch also addresses other vulnerabilities.
Key takeaways for defenders:
Happy hunting and patching!
Share this post
We got cookies
We only use cookies that are necessary for the technical functioning of our website. Find out more on here.
OK